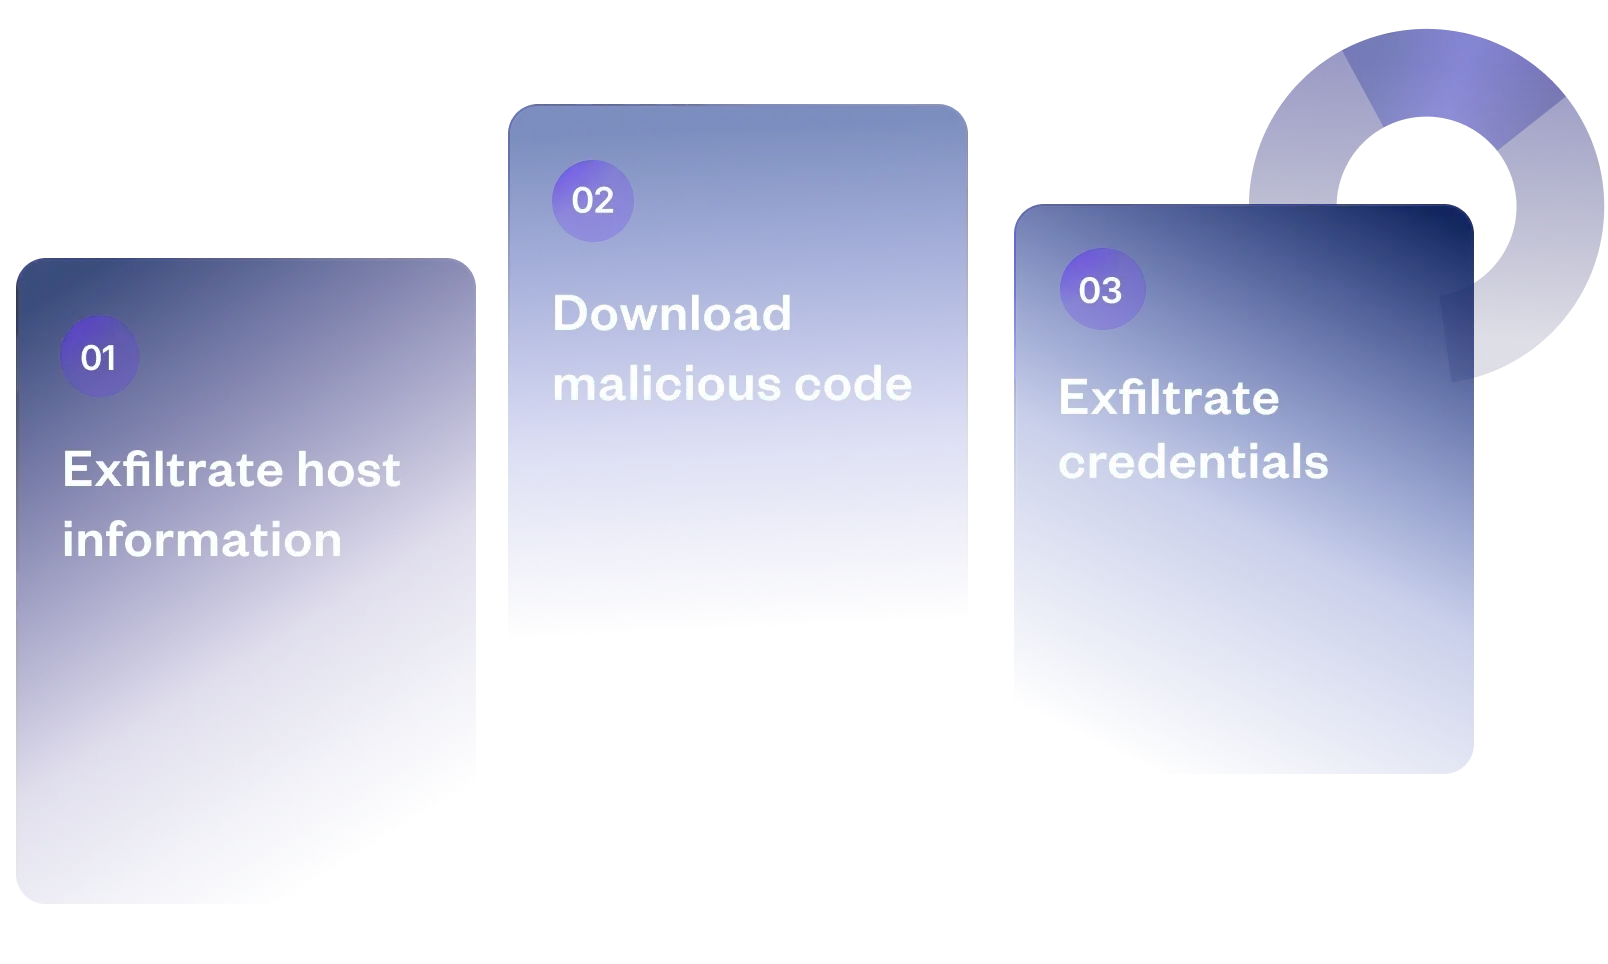
During the month of June, the Checkmarx security research team studied our internal repository of over 385,000 malicious packages found in the wild. Here are the three trending goals of those malicious packages.
Exfiltrate host information – 58.44%
Everyone is a target. More than half of the incidents we studied from our own malicious package repository found malicious packages that sought to exfiltrate everything from operating system information, hostname, mac addresses, and more.
Malicious code downloads – 24.12%
Threat actors continually evolve their methods for tricking users to download malicious code from seemingly secure or trustworthy sources. Ultimately, users download and execute additional malicious code from an external resource.
Exfiltrate credentials – 17.44%
System credentials are a highly prized target of many software supply chain attackers, including passwords, browser cookies, API keys, and more.